A connected charging network can handle resident identities, parking locations, vehicle or account identifiers, session times, energy readings, payment details, support logs, and remote-control messages. Before selecting a system, identify which data it creates, where each item travels, who can see it, and what the building can do if a supplier or account is compromised.
Privacy and cybersecurity are related, but they ask different questions. Privacy concerns the collection and use of information about people. Cybersecurity concerns protecting systems and data from misuse, disruption, or unauthorized access. A supplier’s answer to one does not settle the other.
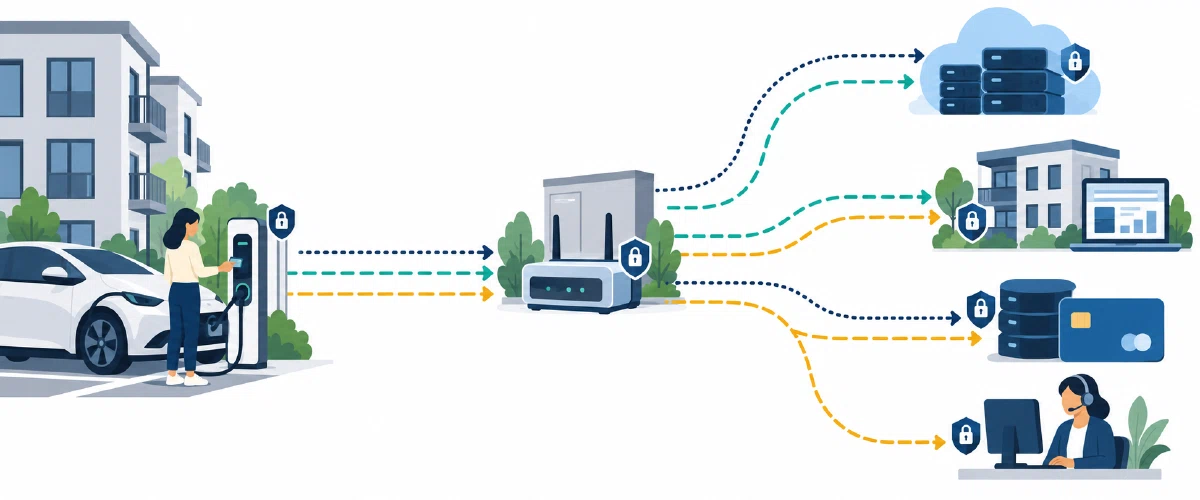
Draw the data path before approving the service
Ask the supplier to map a typical resident session from the charger to every system that receives information. Include:
- resident name, account, access token, or vehicle credential;
- stall, charger, connector, session time, energy, and charge status;
- meter values, tariff, receipt, reimbursement, or payment token;
- charger faults, support messages, remote commands, and diagnostics;
- the property manager’s tools, network operator’s cloud, payment service, utility, and any subcontractor.
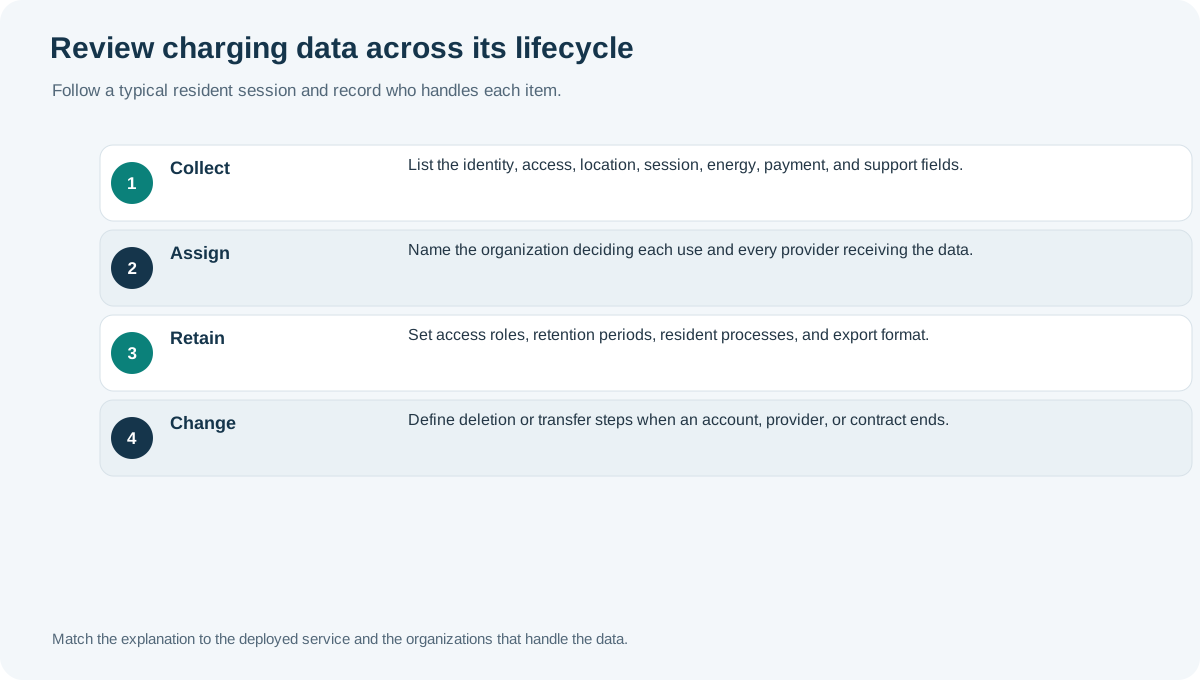
For each field, ask why it is collected, whether the service can work without it, which organizations receive it, how long they keep it, and whether it is sent or stored outside the country. Request a data dictionary and a plain-language resident notice that match the deployed configuration. Do not assume an app, protocol, or data-hosting location tells you who has legal control or who can answer a resident’s request.
Check privacy responsibilities and contract terms
Put these questions in the procurement review:
- Which organization decides why resident information is collected, and which organizations process it on that organization’s behalf?
- What information is necessary for access, charging, support, billing, and security? Can optional telemetry or location history be disabled?
- Which service providers and subcontractors receive the data? Where do they process it, and how will the building learn about a new provider or transfer?
- What are the retention, deletion, export, account-transfer, and resident-access procedures?
- Who answers access or correction requests, complaints, and incident reports?
- Which contract terms control the provider’s use of data, comparable safeguards, security incidents, and cooperation at termination?
The Office of the Privacy Commissioner of Canada’s published guidance on assessing third-party service providers gives organizations subject to PIPEDA best practices for reviewing providers that handle personal information. The OPC is accepting comments through 4 December 2026 while it evaluates whether amendments are needed; the guidance is not itself a new legal requirement. It does not establish that every condominium, landlord, or charging service is covered by PIPEDA; provincial and territorial rules and the building’s role also matter. In the United States and United Kingdom, identify the applicable national and local requirements with qualified privacy advice before relying on a generic vendor statement.
In England, Scotland, and Wales, separate smart-charge regulations set device-level requirements for covered private charge points sold for domestic or workplace use, including security and consumer information. Their product scope does not establish that a whole apartment network meets every privacy or cybersecurity obligation, and the guidance does not cover Northern Ireland or public charge points.
Great Britain’s Department for Transport opened a separate consultation on cyber security for public charge points on 29 October 2026, with comments due 20 December 2026. It is a proposal, not current law, and its public-charge-point scope does not decide whether a particular apartment garage is public. Check the final position and actual site classification before treating it as applicable.
Review system security across its parts
Request a responsibility map for the charge points, local network, cloud management system, building controls, payment service, and remote support. Ask the supplier to explain and demonstrate:
- individual accounts, least-privilege roles, administrator approval, and logs of privileged actions;
- how credentials and certificates are stored, renewed, disabled, and recovered;
- how firmware and security updates are authenticated, tested, scheduled, and supported;
- how vulnerabilities are reported, assessed, fixed, and communicated;
- how remote access is approved, limited, monitored, and ended;
- what data and control paths are separated from other building networks;
- what happens to configurations, event logs, and session records after a system restore or replacement;
- who coordinates response, resident communication, investigation, and recovery after an incident.
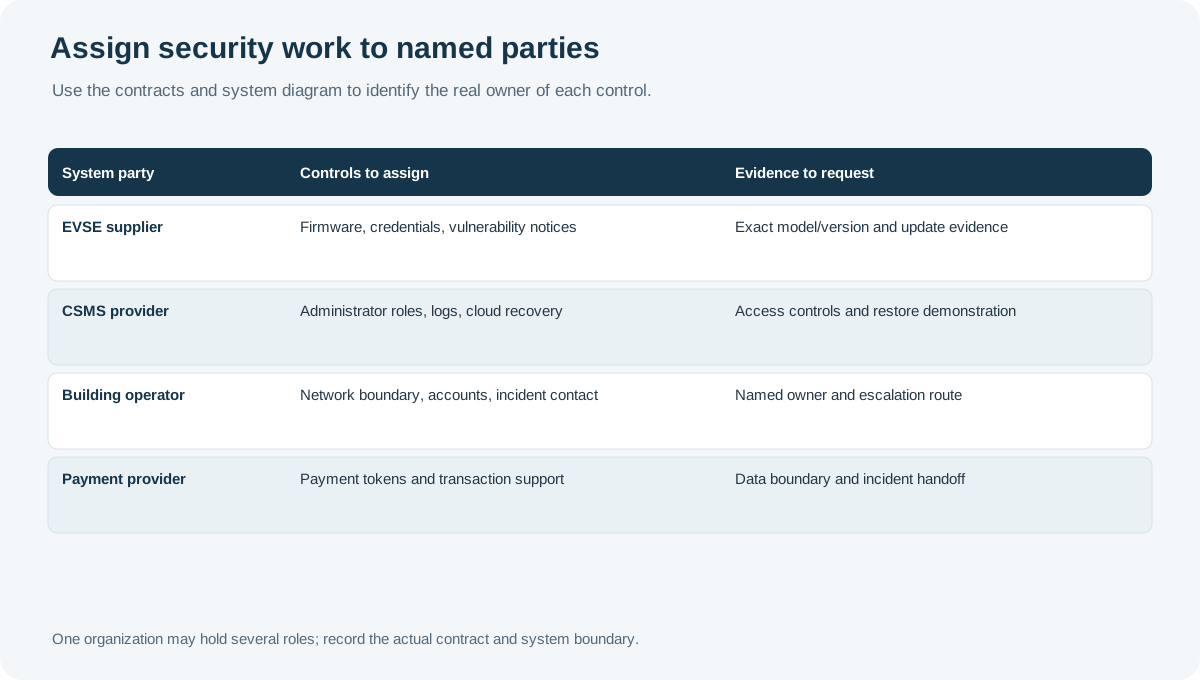
Use the actual charger model, firmware, software service, and contract in the review. The Open Charge Alliance’s Security Operations Guide Version 2, published 22 September 2026, offers operational security guidance for charging stations and CSMSs and separates CSMS-provider and charge-point-operator responsibilities. Ask suppliers which practices they apply and what evidence supports their answers; neither the guide nor protocol support proves that a supplier implemented every control or that a building meets a legal standard. A NIST profile can help organize risk questions; its cited EV charging profile is written for extreme-fast-charging infrastructure and is not an apartment compliance checklist.
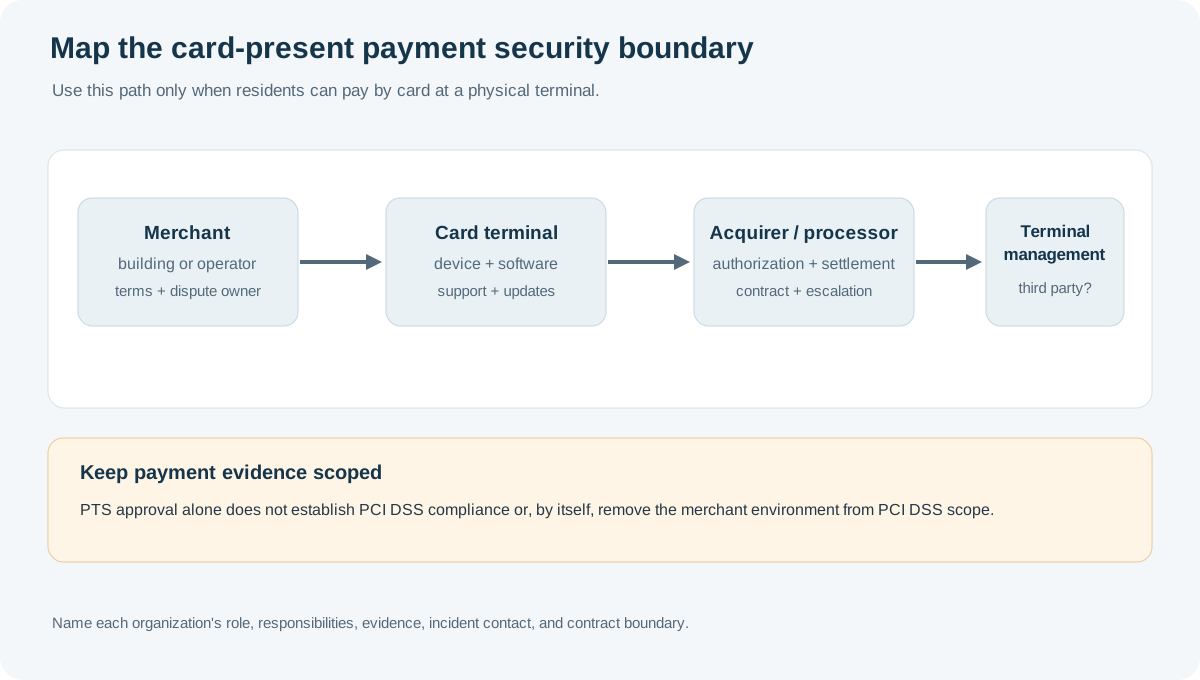
If residents can pay by card at a physical terminal, map that conditional payment path separately from charger networking. Identify the merchant, acquirer or processor, terminal, and any third-party terminal-management service; assign who configures, updates, monitors, and supports each part. PCI SSC explains that PTS approval alone does not establish PCI DSS compliance or, by itself, remove the merchant environment from PCI DSS scope. Confirm the actual payment design and responsibilities with the provider and a qualified payment-security adviser; this question applies only when the deployment captures card-present payments.
Make the answers usable to residents
A privacy notice should explain, in ordinary language, what information is gathered during a charging session, why it is needed, which service providers receive it, how long it is kept, and where a resident can ask questions. Give residents a non-app contact for access or support where the service design permits one. Avoid collecting vehicle or location detail simply because a device can provide it.
The building should be able to explain who controls accounts and whether a resident’s access survives a network outage or a supplier change. Use the separate guides to connected-system requirements and uptime and vendor exit to make those responsibilities part of the service plan. If session and energy records will support a resident kWh charge, review the relevant U.S. metering guide or Canadian approval guide as well.
Checked: 9 November 2026. Privacy rules, device-security requirements, and vendor practices vary by jurisdiction and product; confirm current applicability and contracts before deployment.